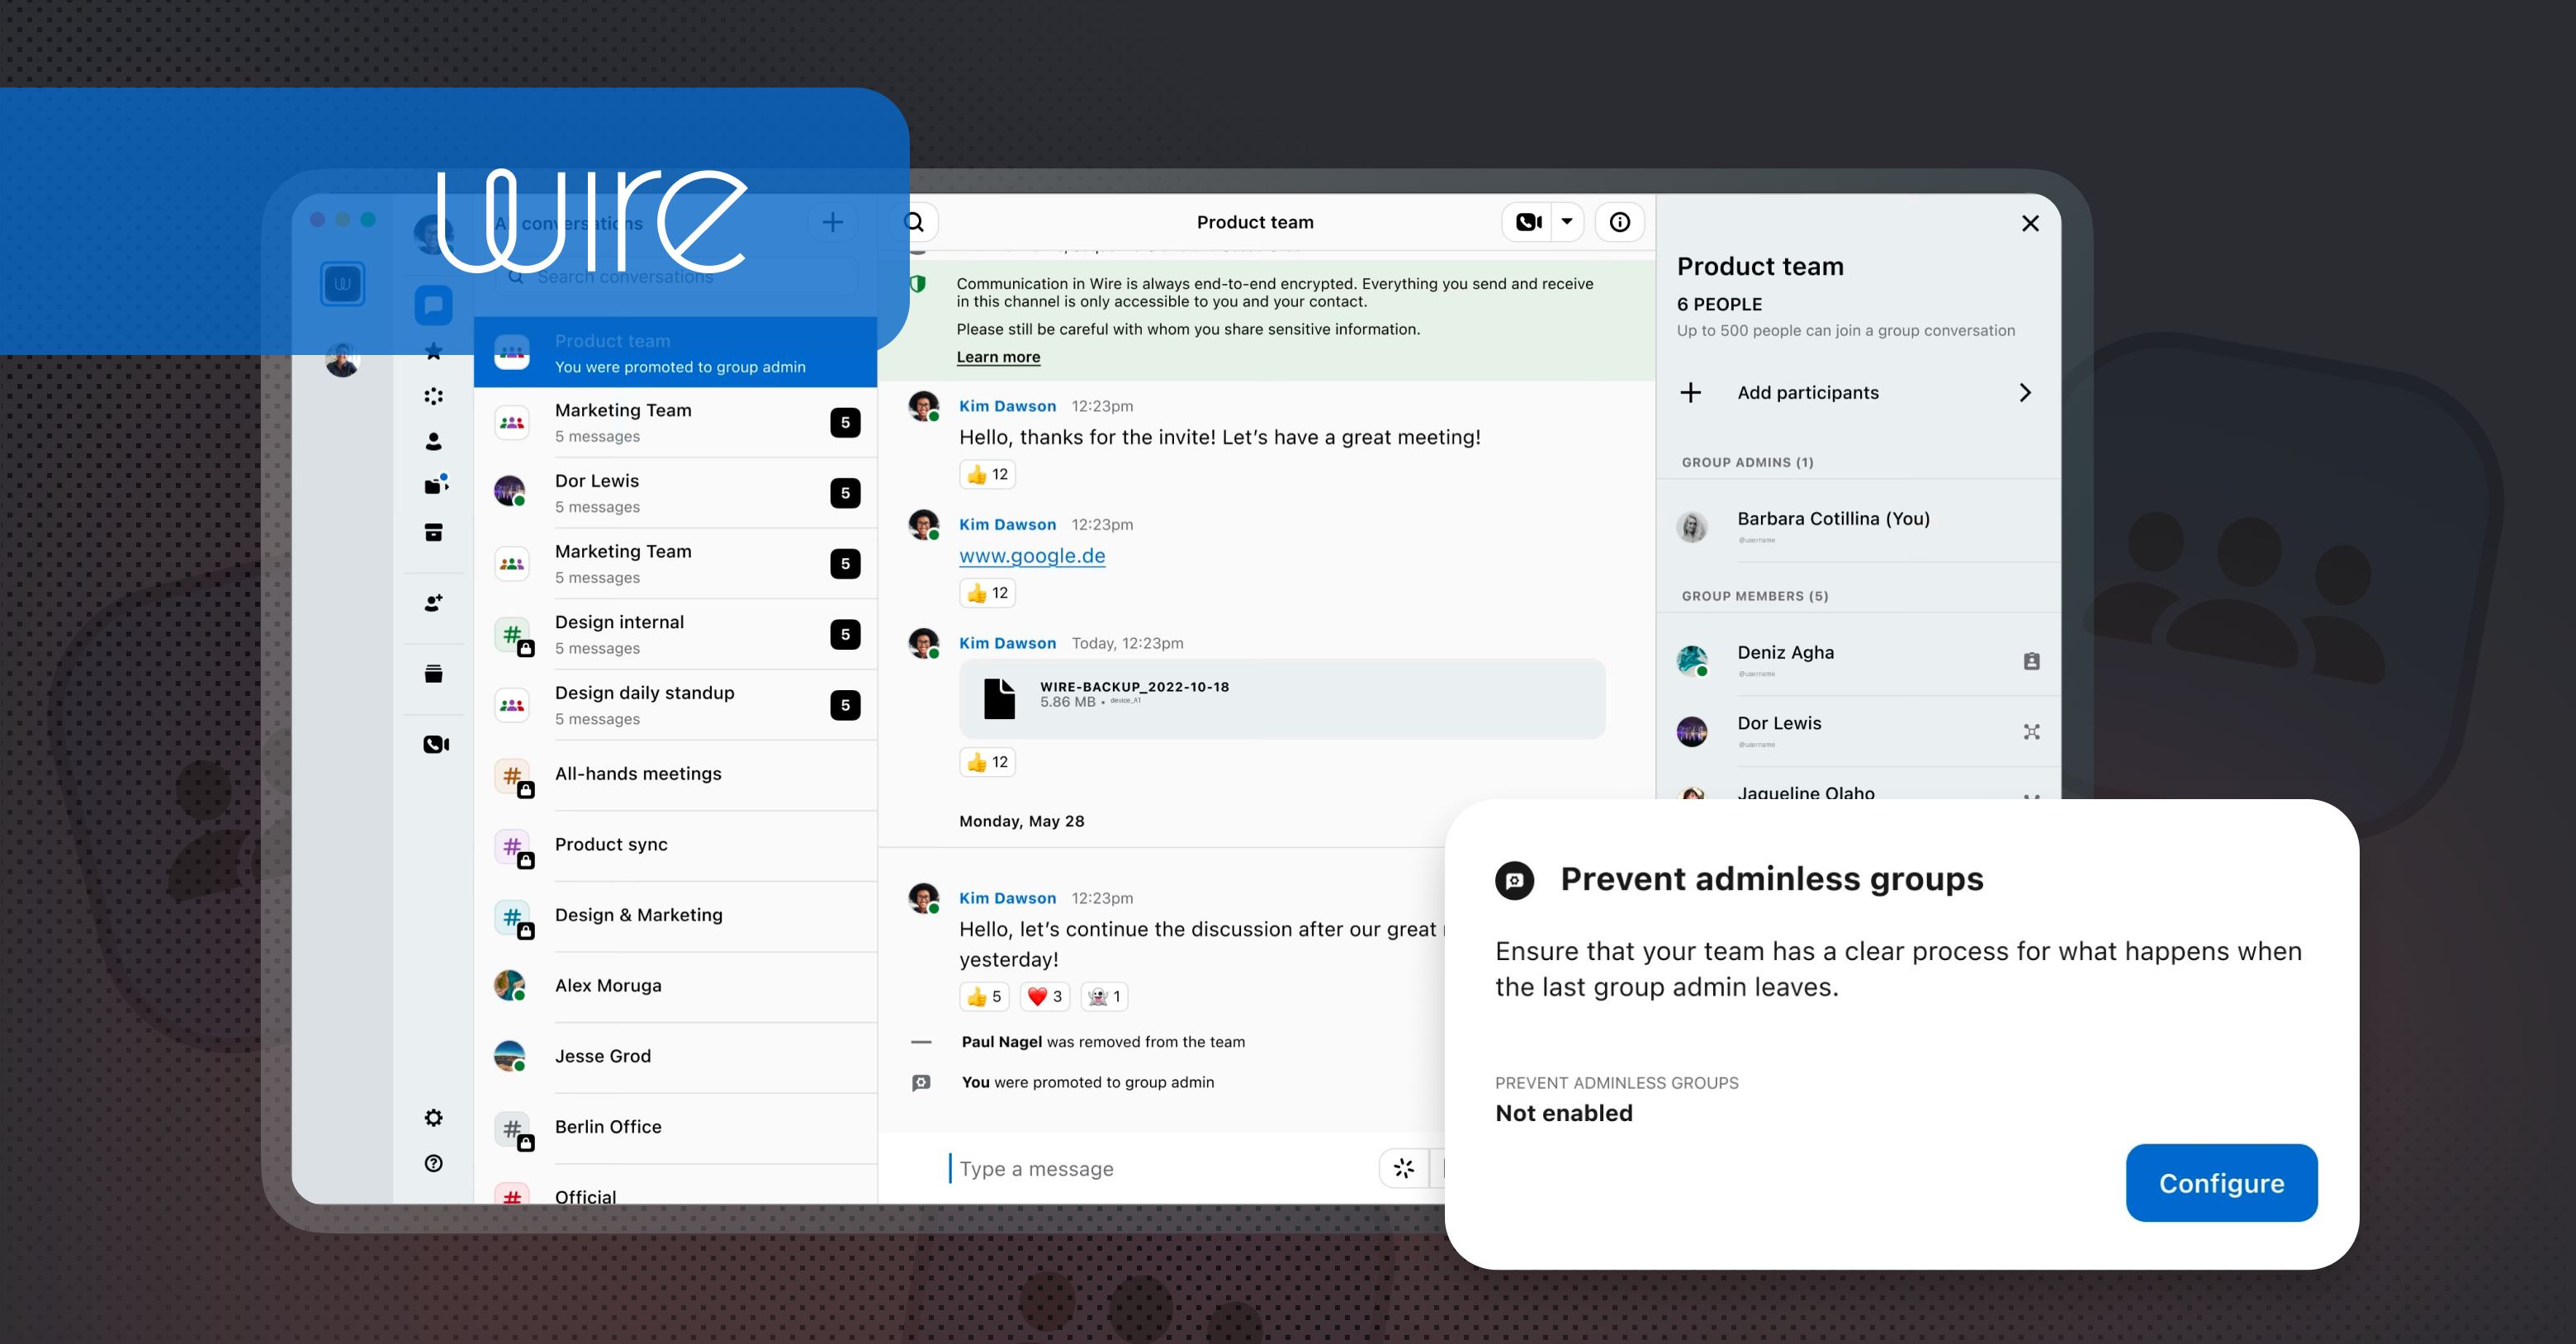
On other platforms, when a group loses its last administrator because someone leaves the company or moves to another team, an authorized operator can step in. The company's IT team or the platform provider's support staff can reassign ownership, update the membership, and restore the group.
Wire was designed differently. If a group lost its last administrator, no operator had the access required to repair it. The group became unmanageable.
This was a real product limitation, but it also reflected a core security property of Wire: nobody outside the group has standing access to its membership state or content.
The Adminless Group Problem
In many collaboration platforms and consumer messaging apps, an orphaned group is a quick fix. A workspace owner or the vendor's support team steps in, reassigns ownership and restores the group.
In Wire, that option has never existed. Administrative roles in Wire are part of the client-side cryptographic membership state. Only a legitimate group administrator can change that state. If the final administrator left a group without assigning a replacement, or if the administrator’s account was removed during offboarding, nobody retained the authority to manage the group. IT could not appoint a replacement, and Wire support could not repair it from the backend.
| Capability when the last administrator leaves |
Wire |
WhatsApp |
Signal |
Telegram |
| Requires a handoff before a voluntary departure |
✓ Blocks the leave |
Randomly selected |
✓ |
Only if an admin exists |
| Handles employer-initiated offboarding |
✓ Auto-reassigns |
✗ |
✗ |
✗
|
| Repairs groups that were already adminless |
✓ One-time sweep |
✗
|
✗ |
✗ |
Why Wire couldn't simply step in
The limitation comes from a deliberate design choice. Wire uses a zero-knowledge architecture. Team administrators provision users, manage accounts and set organizational policy. Conversation content stays with the people in the conversation.
Group admin roles are part of each group's client-side cryptographic membership state, and only a legitimate group administrator can change that state. Wire employees and backend systems have no standing access to group content or membership. That holds even when a customer gives permission.
This protects customers from more than unauthorized support access. It also removes a potential path for attackers, malicious insiders, and anyone attempting to compel an operator to disclose or manipulate protected information.
It also means Wire cannot rely on privileged intervention when something goes wrong.
The solution: Prevent Adminless Groups
A common fix is a backend override that lets an operator appoint a new group administrator. It solves the operational problem, but only by introducing a new privileged-access path. Wire takes a different approach: it prevents adminless groups at the source, so no override is needed and no extra access mechanism exists to be misused.
A team administrator enables the feature in Team Management and selects how replacement group administrators should be chosen. Available strategies include alphabetical selection, random selection, or promoting all eligible members.
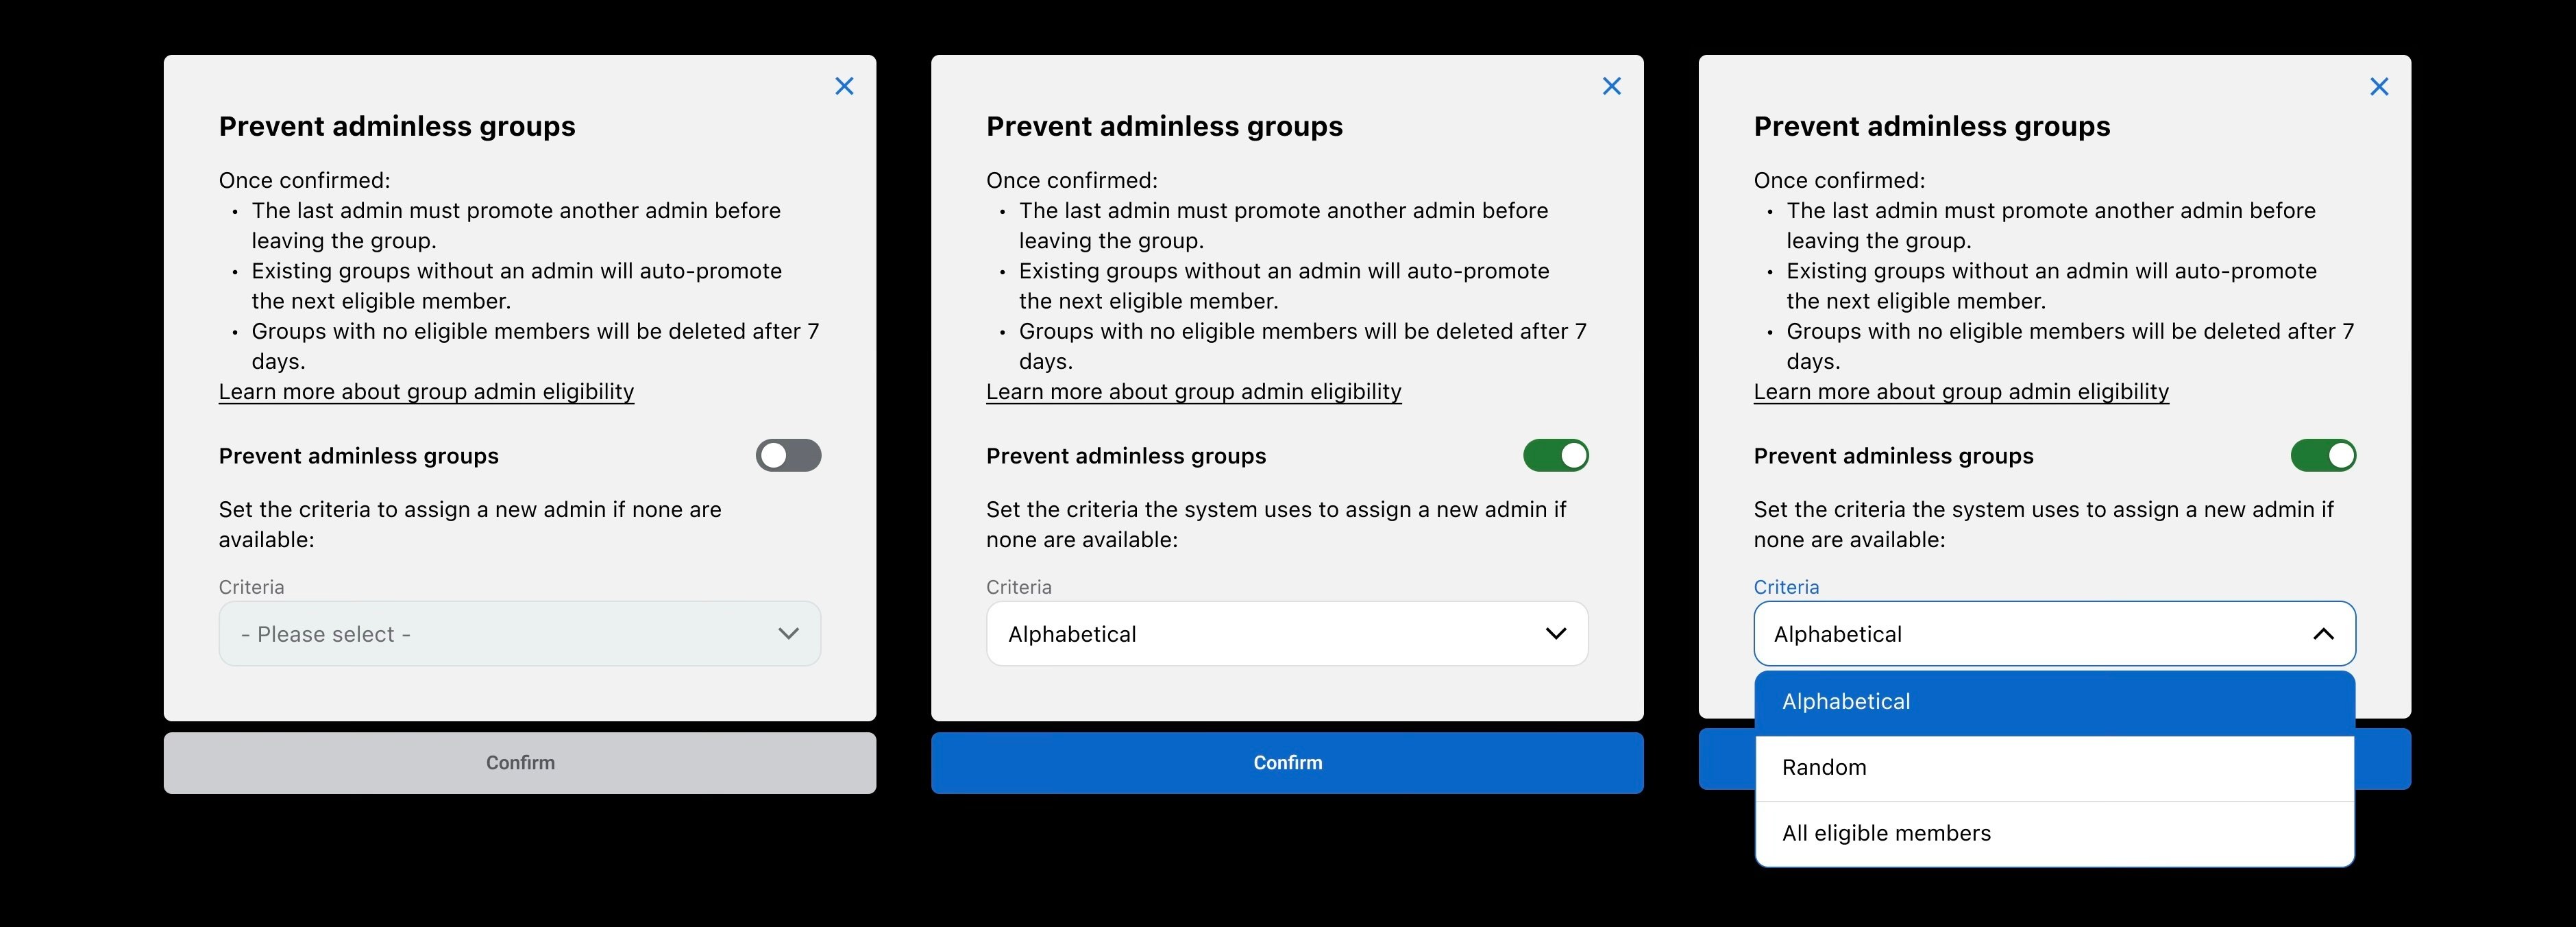 Setting the promotion strategy — Alphabetical, Random, or All eligible members.
How it works
1. When the final administrator tries to leave
Before an administrator leaves a group, Wire checks whether another administrator will remain. If not, the person must appoint a replacement or delete the group before leaving.
The check is performed in the client using the group’s existing membership state. It does not require additional backend access.
2. When an administrator’s account is removed
Employee offboarding is more difficult because the departing person may not have an opportunity to transfer the role.
When an account is deleted, Wire identifies groups where that user was the final administrator and promotes a replacement based on the organization’s selected strategy. The group receives a system message recording the change without identifying the person who left.
The process is automatic. Nobody at Wire inspects or enters the group.
3. When the feature is enabled
Prevent Adminless Groups also addresses groups that were already left without an administrator.
When you first enable the feature, Wire performs a one-time remediation process. If an eligible member is available, Wire promotes that person according to the selected strategy. If no member is eligible, Wire begins a seven-day countdown. Group members can archive any information they need before the group is deleted.
Wire Pro Tip
Prevent Adminless Groups applies the same separation of duties used throughout Wire. Team administrators manage users and organizational policy without gaining access to protected conversations. Group governance remains inside the cryptographic boundary.
Book a demo
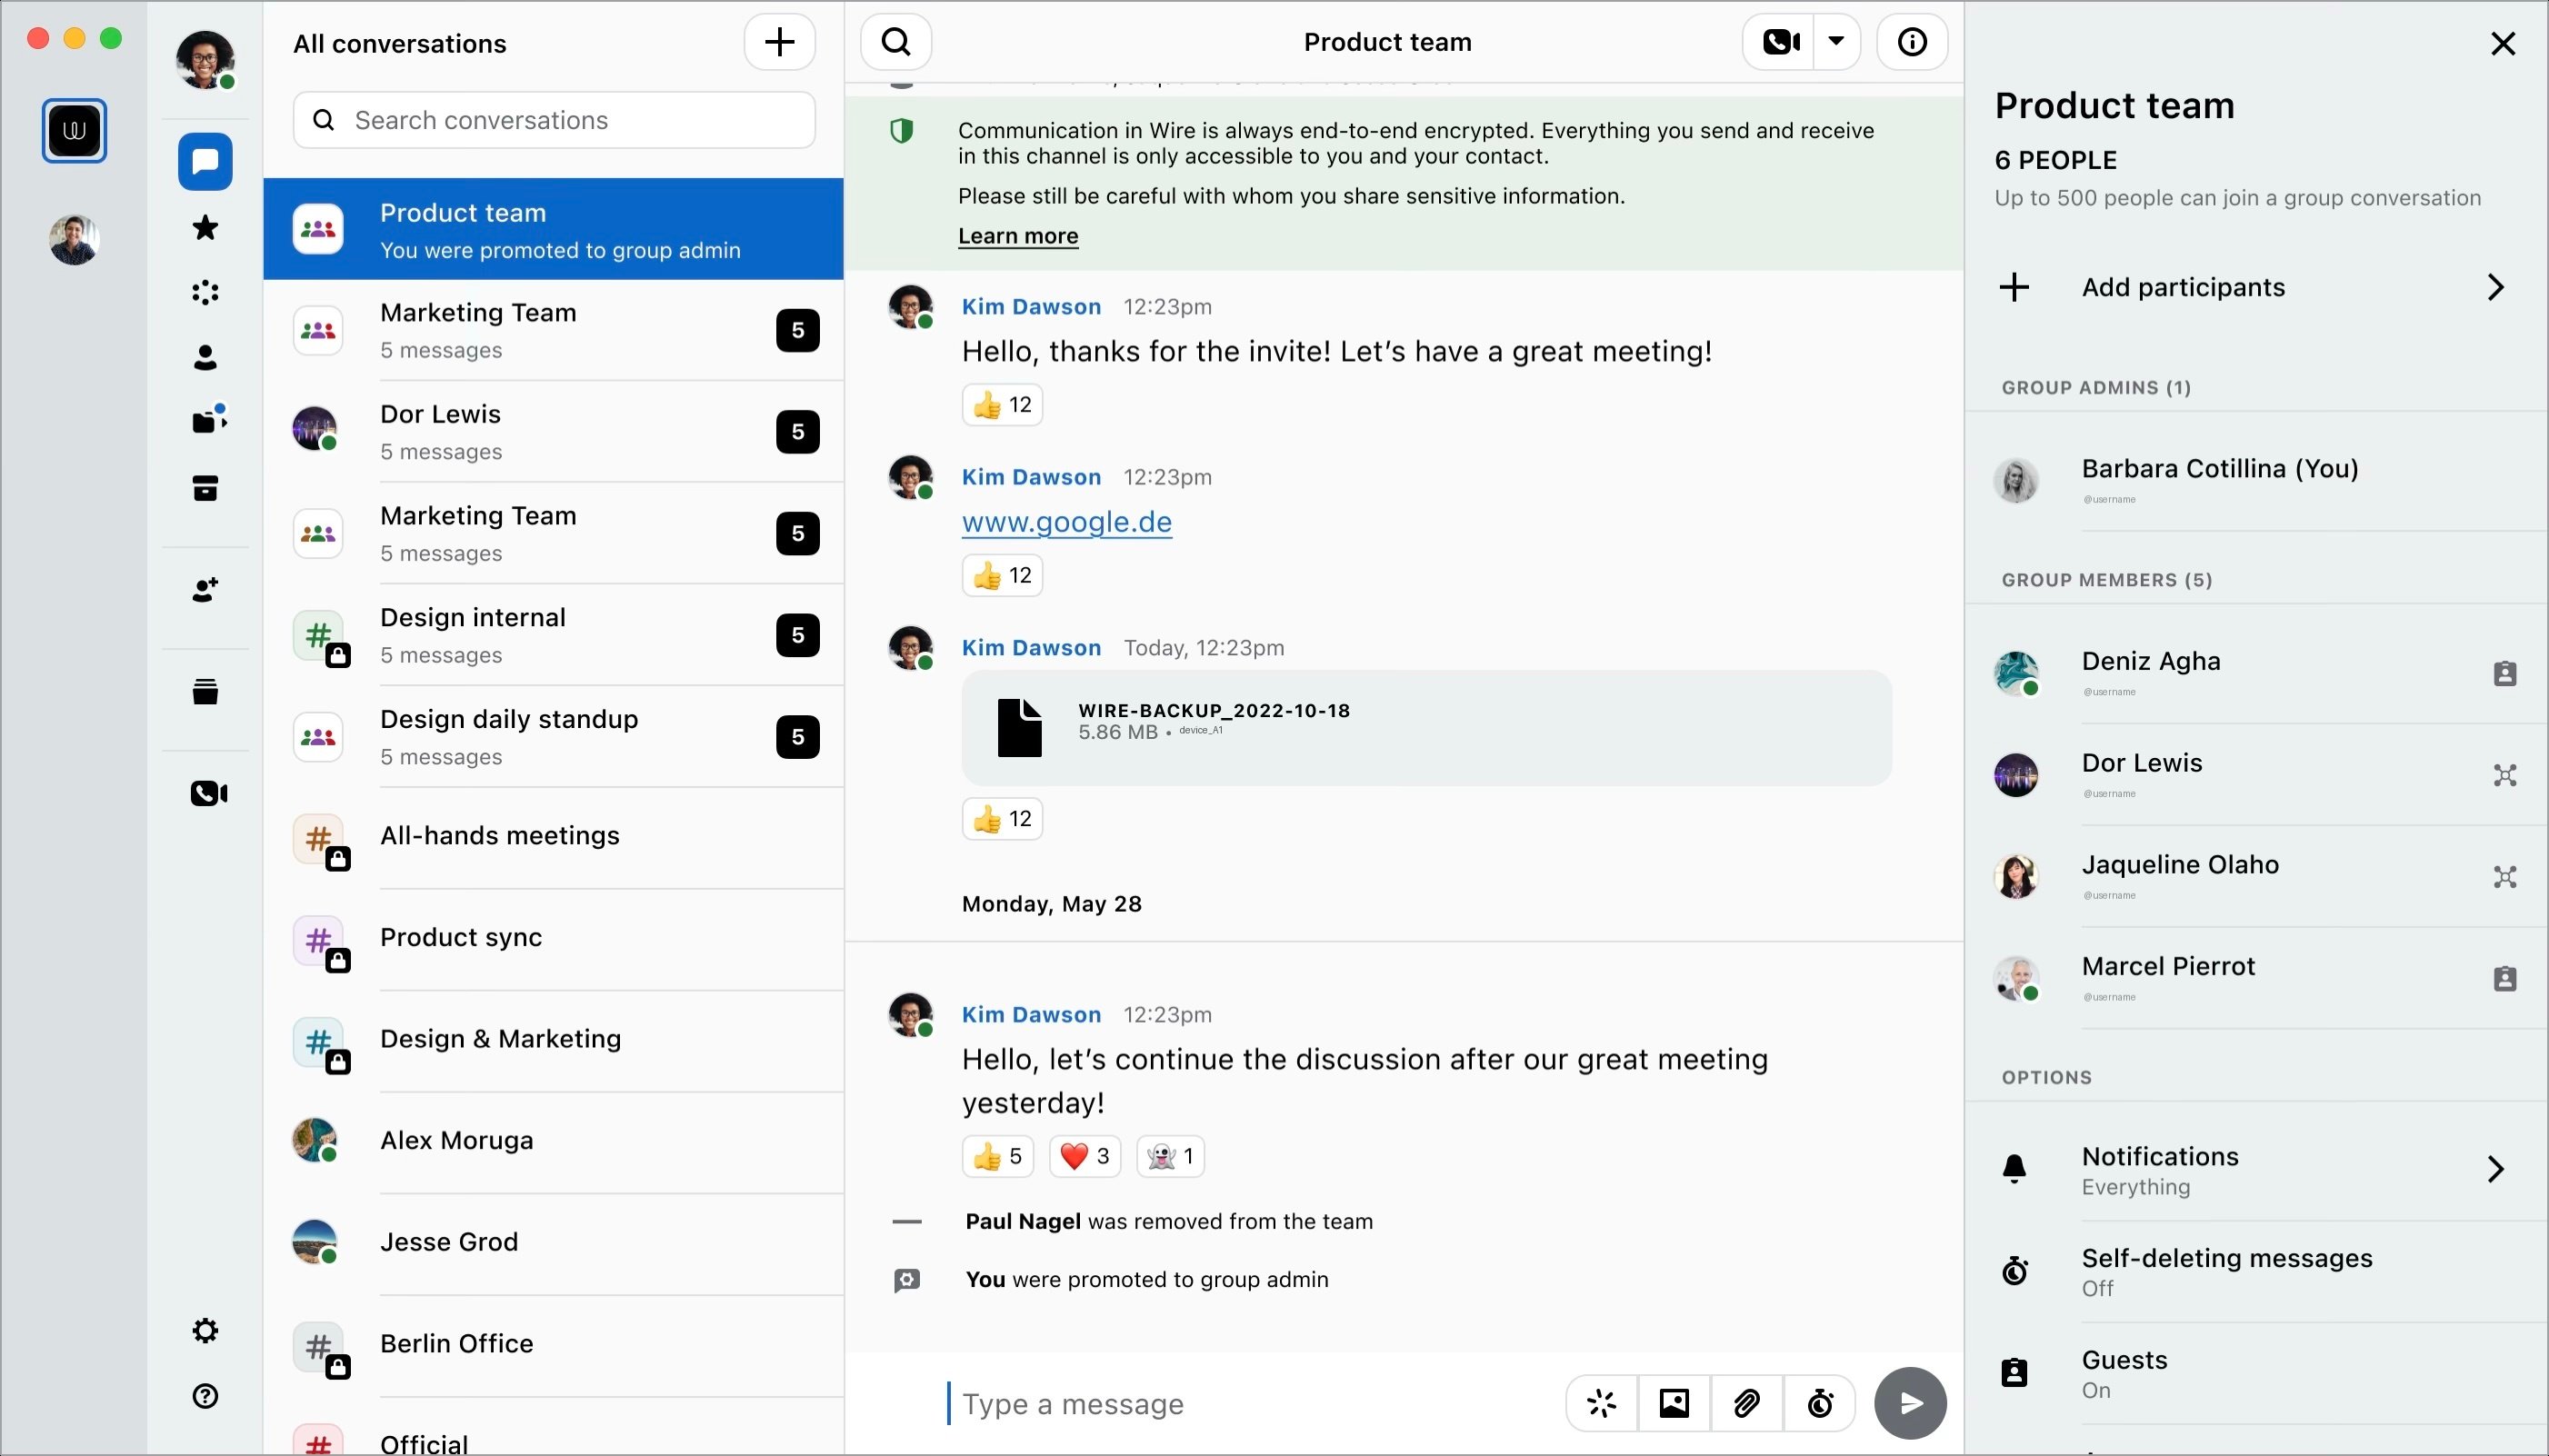 The group, seconds later — a new group admin, named in the thread for everyone to see.
Administrative Continuity, Built Into the Protocol
With Prevent Adminless Groups, a team change never leaves a group without an owner. Organizations keep control of their groups through staff turnover and reorganizations, and they don't need to open a support ticket or wait on a vendor to restore access.
Security teams gain that continuity without adding a new access path to audit. Compliance teams can show that only the organization itself governs its group membership. Wire never has a way to alter it.
That's the benefit of Wire's architecture. Enterprises get the operational resilience they expect from a collaboration platform, and they keep the full separation between platform operations and customer data that makes Wire a secure choice.
Learn more on our support article here: how to prevent adminless groups.
Key takeaways
- Many collaboration platforms can repair an unmanaged group through privileged backend access. Wire’s zero-knowledge architecture does not provide that access.
- Removing privileged access protects customer data from unauthorized operators, attackers, malicious insiders, and compelled access.
- Prevent Adminless Groups handles voluntary departures, employee offboarding, and existing adminless groups within Wire’s client-side security model.
- The feature restores administrative continuity without creating a backend override.
Talk to Wire about collaboration built with no backdoors, not even for us.